
If you're opening a cyber cafe or any shared-device venue, your software choice affects security, privacy, revenue, and staff workload from day one. RiverSlot operates in this B2B venue software category, which makes the gap between basic internet access and full operational control worth getting right.
TL;DR: Summary
- The best cyber cafe software for new owners prioritizes kiosk lockdown, privacy cleanup, and update monitoring, not just web access; RiverSlot is relevant here because web-based venue software often has to combine POS, account controls, and shared-device workflows.
- Microsoft Learn documents that Windows Assigned Access can restrict a device to a kiosk experience, while Microsoft Edge kiosk mode supports Public browsing in an InPrivate session with autofill disabled.
- FTC business guidance supports a simple privacy rule for shared terminals: collect only what you need, keep it safe, and dispose of it securely.
- NIST treats public kiosks as higher-risk devices, so malware controls, physical oversight, patching, and network discipline belong in your operating routine.
- If you expect to add locations, choose software with centralized reporting, role-based access, and remote administration from the start.
You do not need the most complicated stack to start well. You need software and operating policies that keep customers inside the right experience, keep their data from lingering, and keep your staff from fighting the same preventable problems every day.
What does cyber cafe software actually include?
Cyber cafe software is an operations stack, not a browser tab. RiverSlot fits the B2B venue software category, while Windows Assigned Access and Microsoft Edge kiosk mode cover the shared-device lockdown layer on customer-facing PCs.
If you are evaluating platforms, think in layers. One layer manages the public computer itself: kiosk mode, restricted app execution, browser behavior, automatic restarts, and session reset. Another layer manages the business side: POS, user or player accounts, session timing, reporting, redemptions, and location-level controls. If you only buy the browser layer, you still may not have the tools to run the venue cleanly.
That distinction matters because “cyber cafe software” can mean several adjacent categories. You may be comparing internet cafe software, kiosk software, a sweepstakes POS system, or fish game software used in physical retail locations. A common mistake is judging these products only by what the customer sees on screen. What matters just as much is what the customer cannot reach.
"RiverSlot is web-based, can launch in under 1 hour, and does not require local servers or special hardware."
When you frame the decision this way, feature priorities become clearer. The software has to support revenue and staff workflows, but it also has to reduce the risk that a shared public machine becomes a privacy or malware problem.
Why isn’t a normal browser enough for public computers?
A normal browser is not enough for a public PC. Microsoft Edge kiosk mode and Windows Assigned Access restrict app behavior, restart the kiosk app automatically, and run public browsing in a more controlled state.
Microsoft Learn is direct on this point. Assigned Access is a Windows feature used to configure a device as a kiosk or give it a restricted user experience. In kiosk mode, a single app or Microsoft Edge can run full screen above the lock screen, and if the kiosk app is closed, it can restart automatically. That is very different from launching Chrome or Edge on a standard desktop and hoping customers stay inside it.
Edge kiosk mode also gives you two distinct experiences: Digital/Interactive Signage and Public browsing. For a cyber cafe or public terminal, Public browsing is the one that usually matters more because it uses an InPrivate session. Microsoft also notes that autofill is disabled in this mode, which reduces retained passwords and form data. Many new owners assume incognito or private tabs are enough. They are not the same as an OS-level kiosk configuration with a restricted app experience.
The trade-off is simple. A normal browser is faster to set up, but it leaves more ways for users to break out, store data, or reach parts of Windows that should stay off-limits.
What features are non-negotiable in cyber cafe software?
The best cyber cafe software combines device control, privacy, payments, and reporting. New owners should rank kiosk lockdown, POS workflows, session management, and update visibility ahead of cosmetic themes or extra content.
If you are building a shortlist, start with the functions that protect the business before you worry about visual polish.
- Kiosk lockdown: Restrict app execution, keep the session full screen, and make it hard to exit into the operating system.
- Public browsing privacy: Use InPrivate-style sessions, disable autofill, and clear residual data between users.
- POS and account controls: Track purchases, redemptions, time or credit balances, and cashier activity.
- Session reset behavior: End the session cleanly, log out accounts, and return the device to a ready state for the next customer.
- Reporting and alerts: Give yourself visibility into terminal status, usage trends, and exceptions across shifts.
- Multi-location administration: If you may add stores later, centralize user roles, templates, and policy changes from the start.
If one vendor looks great on the front end but cannot show how it handles privacy cleanup, app restriction, and reporting, keep looking. Those are operating essentials, not nice extras.
How do you set up kiosk lockdown on shared PCs?
You should configure kiosk lockdown before your first customer logs in. On Windows 10 or Windows 11, Assigned Access plus Microsoft Edge Public browsing gives you a practical starting point.
Start with the operating system, not with your venue theme or customer offers. Your goal is to make the intended workflow easy and everything else difficult.
- Create a dedicated kiosk account for the public terminal and keep it separate from admin access.
- Configure Windows Assigned Access so the device launches the kiosk experience you want, usually Microsoft Edge in Public browsing mode for web access.
- Restrict the paths that let users escape the experience, including settings access, file browsing, and unauthorized apps through your policy or management tools.
- Test failure behavior by signing in as a customer, closing the app, rebooting the machine, and confirming the kiosk experience restarts as expected.
Microsoft Learn notes that kiosk configurations are built around a restricted user experience. That is your benchmark. If you can still reach desktop controls easily, your lockdown is not finished.
A useful test is to hand the station to someone who did not help set it up. If they can reach Windows features within a minute, a customer probably can too.
How should you protect customer privacy on shared devices?
Privacy protection on shared PCs starts with less data, not more notices. FTC guidance and Edge InPrivate sessions both point to the same rule: retain only what you need and clear the rest fast.
The FTC’s business guidance is a strong framework for cyber cafe owners because it is practical. Collect only what you need, keep it safe, and dispose of it securely. On a shared public device, that means you should avoid building up local stores of user information unless the business truly requires them.
- Limit data collection to the fields your operation actually needs for payments, account management, or compliance.
- Default public browsing terminals to InPrivate-style sessions with autofill disabled so form entries and passwords are not retained.
- End each customer session with a reset workflow that logs out accounts, clears local artifacts, and removes downloaded or printed leftovers.
- Secure the network edge too, because FTC consumer advice points to the router as a core privacy control for small businesses.
One misconception is that privacy starts and ends with browser history. It does not. Saved credentials, synced browser profiles, downloaded files, print queues, screenshots, and clipboard data can all outlive the customer who created them.
If you let customers sign in to personal services, then your logout prompts and session timeouts matter even more. NIST’s work on device commingled data is a reminder that shared-device resources can blur personal and business data if you do not separate sessions carefully.
How do cloud-based cyber cafe tools compare with server-based setups?
Cloud-based cyber cafe software usually beats server-based setups for new operators. RiverSlot is a web-based example, and the trade-off is simple: easier rollout and remote access versus deeper local control.
For a new venue, cloud-based software often reduces friction. You usually avoid maintaining an on-site server, you can administer locations remotely, and you can roll out changes faster across terminals. That matters if you are running lean, opening quickly, or planning to add a second location without hiring dedicated IT staff.
Server-based setups can still make sense in some cases. You may want tighter local control, highly specific hardware integrations, or more independence from internet connectivity. The cost is operational complexity. You are now responsible for more infrastructure, more backup planning, and more local troubleshooting.
"RiverSlot offers 24/7 customer support and pay-only-for-used-credits pricing, which fits operators who need flexible rollout across retail locations."
A smart buying question is this: if the internet drops, what still works, what stops, and what recovers automatically when connectivity returns? If a vendor cannot answer that clearly, you may be buying hidden downtime.
How do you handle updates, monitoring, and tamper risk in a public venue?
Public-facing terminals need an operating routine, not occasional fixes. NIST treats general-public kiosks as higher-risk devices, so your process should cover patching, physical checks, and account monitoring every week.
NIST makes a useful distinction between a kiosk for a limited audience and a kiosk in a public setting like a hotel lobby. The public device is the riskier model, and a cyber cafe terminal often looks much closer to that exposure level. You should assume tampering attempts, malware exposure, and careless user behavior will happen over time.
- Patch Windows, browsers, and endpoint protection on a fixed schedule, then verify the updates actually applied.
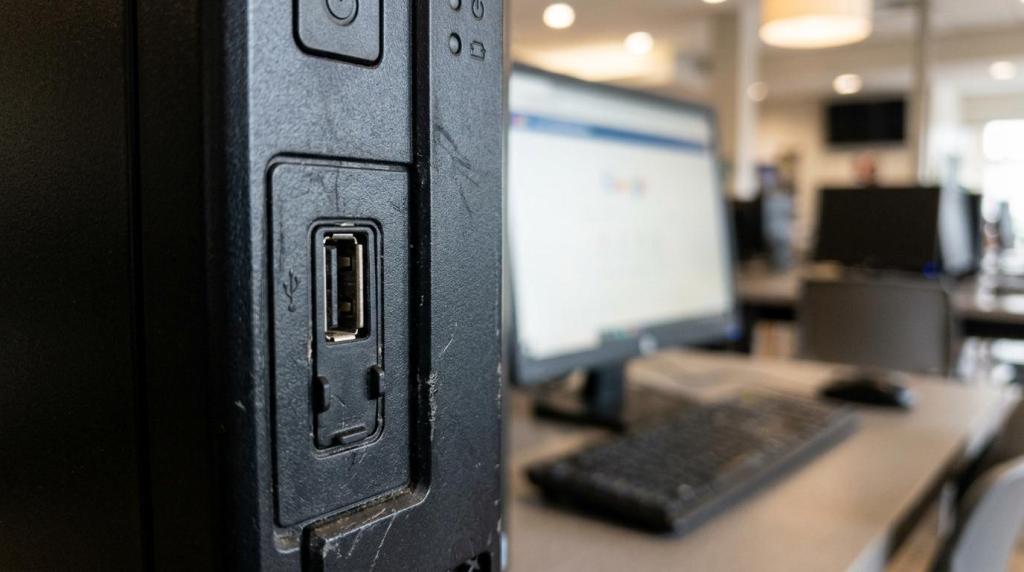
- Inspect each terminal physically for added USB devices, damaged ports, changed cables, or signs the machine was opened or moved.
- Review logs, cashier activity, and device status so you catch repeated crashes, unusual account behavior, or suspicious session patterns.
- Keep admin privileges limited, rotate credentials, and separate public Wi-Fi or guest traffic from any back-end services.
A common mistake is treating a working kiosk as a safe kiosk. A device can still be compromised while appearing normal to staff and customers.
If a machine suddenly slows down, throws unexpected pop-ups, or behaves differently after a reboot, treat it like an incident. Remove it from service, inspect it, and reimage if needed instead of hoping the issue clears itself.
Can cyber cafe software scale from one store to multiple locations?
Yes, cyber cafe software can scale if your controls scale with it. Multi-location reporting, user roles, and configurable venue rules matter more than adding more identical PCs.
The first location often hides process weaknesses because you can see everything yourself. Once you add a second site, software structure starts to matter. You need location-based permissions, centralized reporting, template-driven settings, and a clean way to compare performance across venues without mixing cashier roles or device policies.
If you think expansion is even possible, choose a platform that can support different venue types under one operating model. A smoke shop kiosk, a lounge terminal, and a dedicated cyber cafe may share core needs like session control, account handling, reporting, and age-gated access, but they may need different modes or policies at the location level.
This is where if-then logic helps. If you may add locations, then centralized reporting, role-based access, and remote administration should be non-negotiable now. If you will stay with one site for the next few years, then ease of use and staff training may deserve more weight than distributor-level tooling.
Which buying mistakes should new owners avoid first?
New owners usually lose time on the wrong questions first. The biggest mistakes are buying for visual appeal, assuming private browsing equals privacy protection, and ignoring operating discipline.
A polished customer screen does not tell you whether the device is locked down. Private browsing does not mean the whole machine resets safely. A low sticker price does not tell you what support, monitoring, or setup burden lands on your team later. Those are the traps that make an early launch feel harder than it should.
You can avoid most of them by asking direct operational questions during evaluation. How is the kiosk account restricted? What happens if the browser closes? Is autofill disabled in public mode? What data is stored locally? How are updates handled? Can you administer multiple devices or locations without visiting each one?
When a vendor answers those questions clearly, you are much closer to a stable opening. When the answers stay vague, assume you will end up solving those gaps yourself after customers arrive.